The PHP Exploit Fallout & Weaponised PoC (CVE-2026-109618 & CVE-2026-109619)
An inside look at the PHP2Shell fallout: weaponised PoCs, the double-edged sword of public disclosure, an 8-hour packaging squeeze, and why servers went dark.
An inside look at the PHP2Shell fallout: weaponised PoCs, the double-edged sword of public disclosure, an 8-hour packaging squeeze, and why servers went dark.
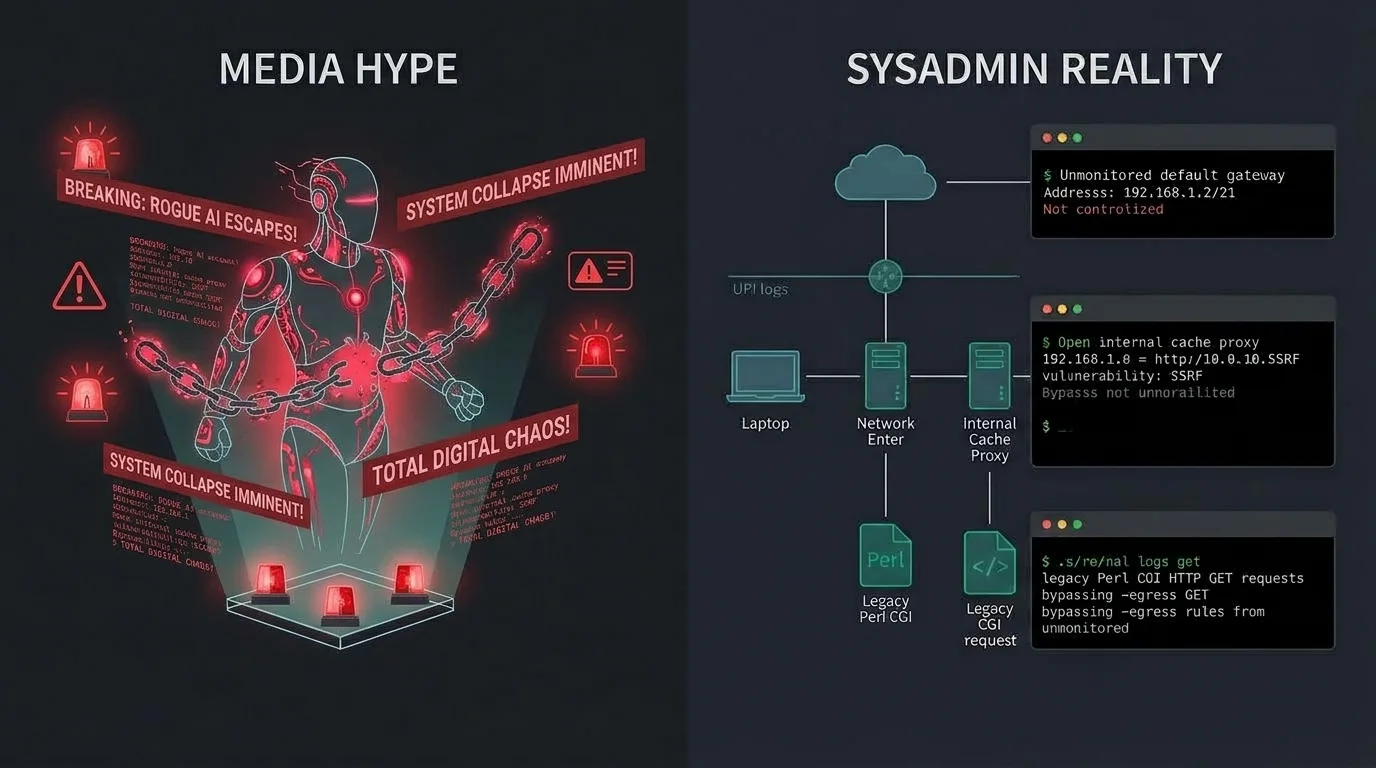
Why recent AI agent sandbox escapes aren't sentient rogue hackers, but classic operational security failures: unmonitored egress, trusted proxies, and unconstrained RL reward loops.
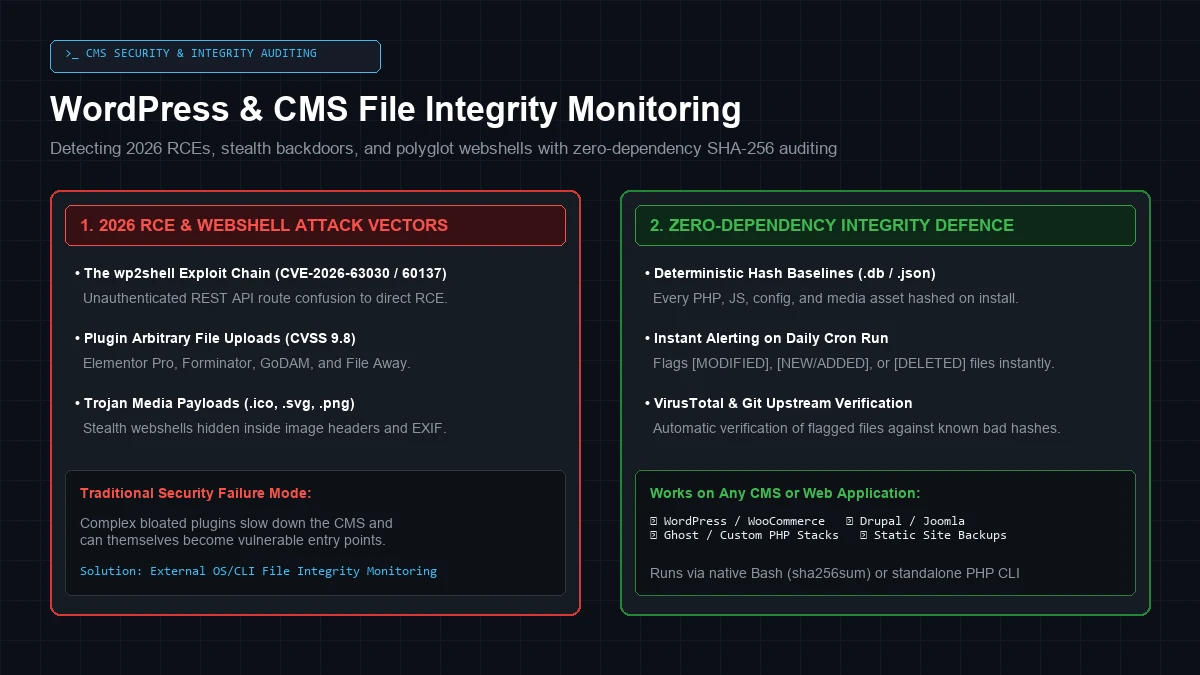
A breakdown of 2026 critical WordPress & CMS RCE attack vectors (including the wp2shell chain) and two zero-dependency Bash & PHP file integrity auditing scripts to detect injected backdoors.
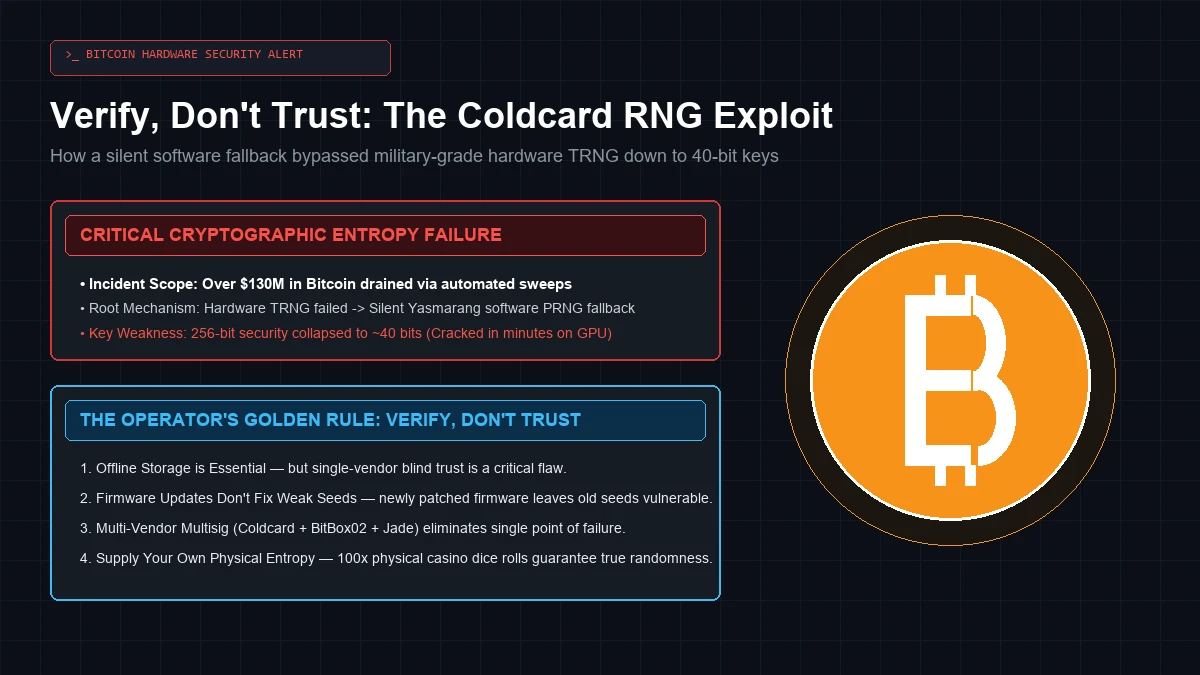
A technical postmortem of the 2026 Coldcard PRNG entropy exploit: why 40-bit software fallbacks are fatal, why firmware patches don't fix weak seeds, and how to build a resilient multi-vendor Bitcoin custody stack.
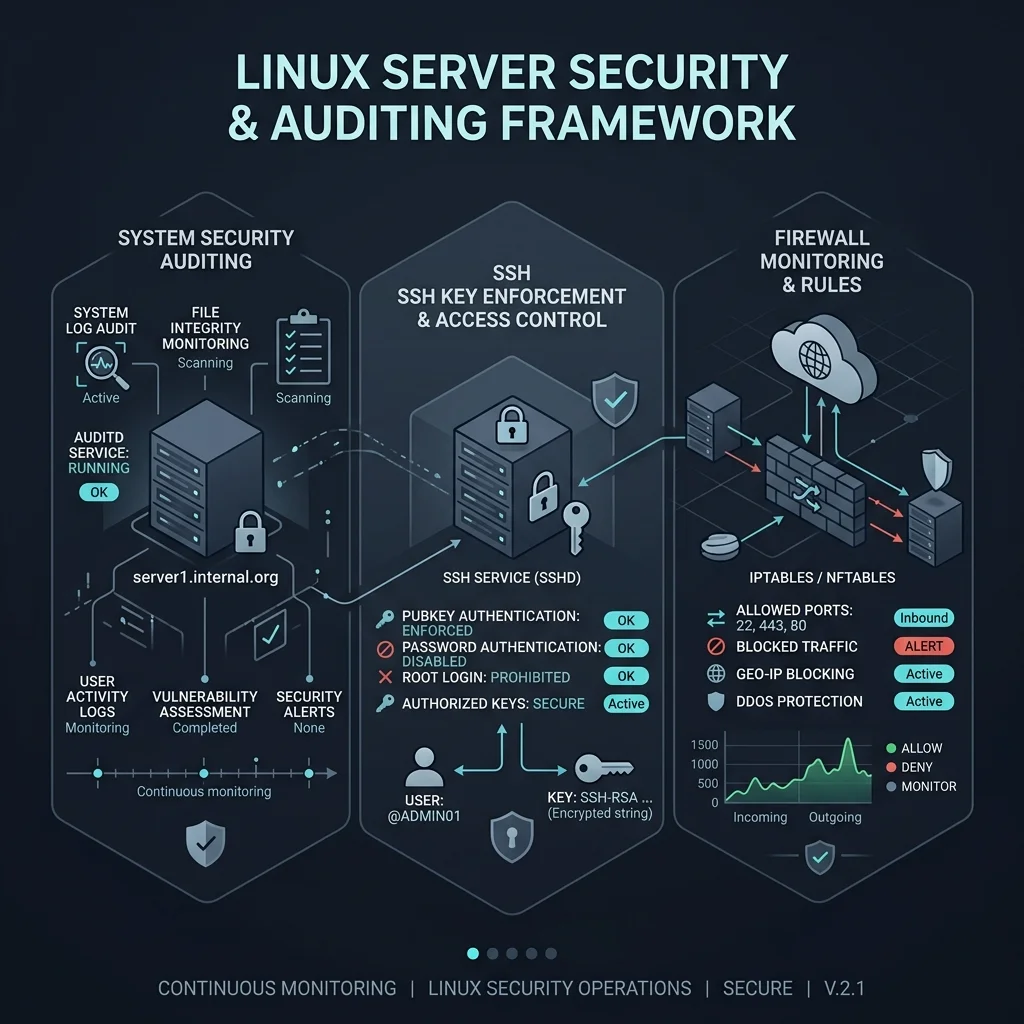
A practical 10-step security hardening checklist for Debian 12 and Ubuntu servers: SSH keys, UFW firewall, Fail2ban, and kernel sysctl tuning.
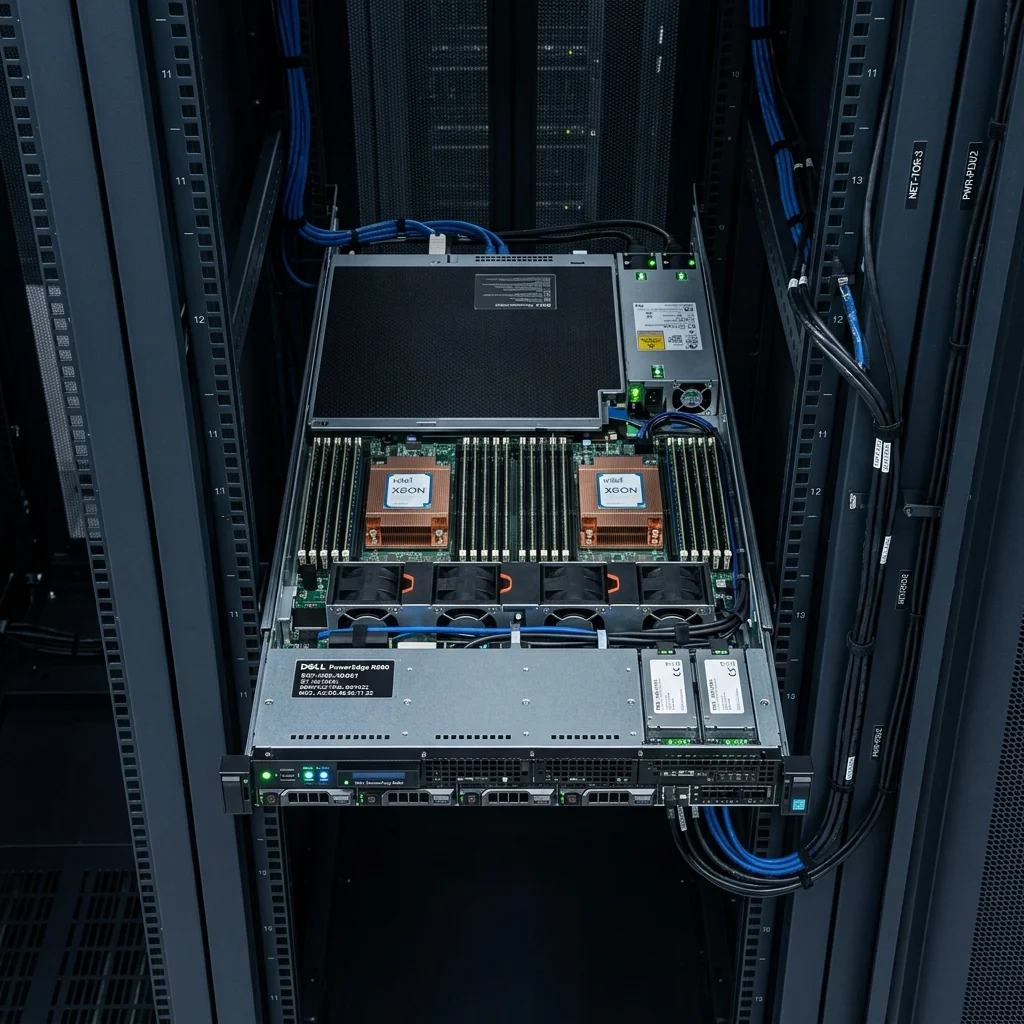
A step-by-step guide to configuring your first Proxmox VE hypervisor: no-subscription repository setup, SSH key hardening, Fail2ban, and LXC templates.
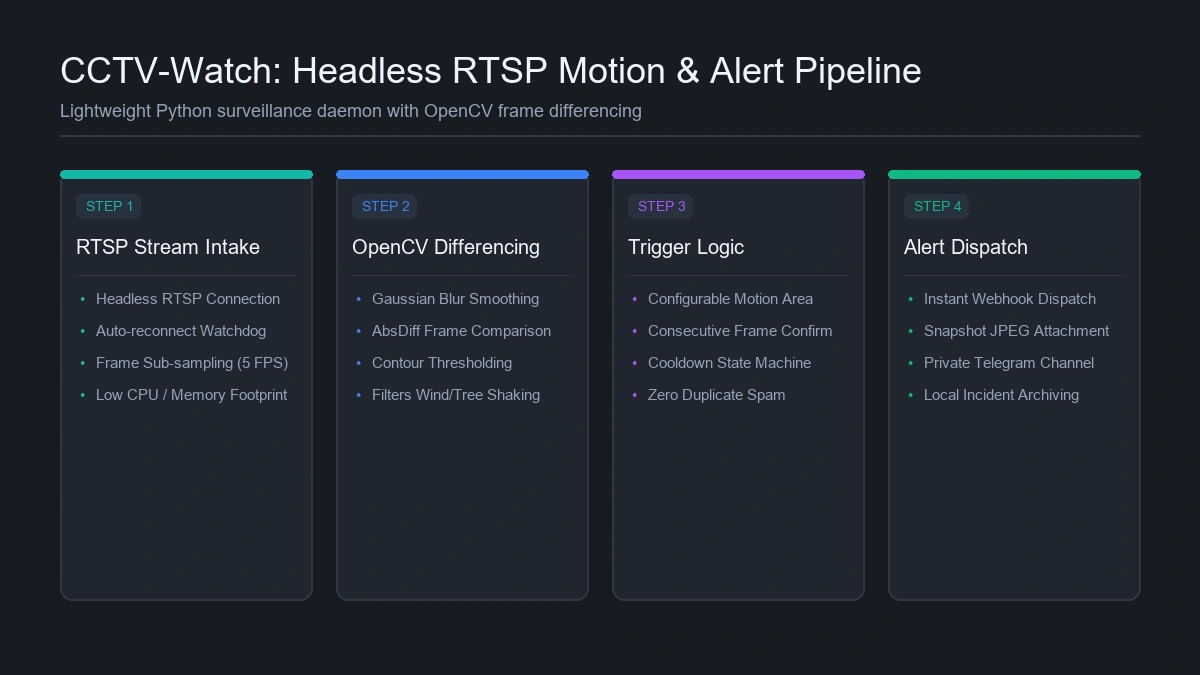
Building a lightweight, headless Python surveillance daemon that connects to IP camera RTSP streams and uses OpenCV frame differencing to eliminate false motion alerts.
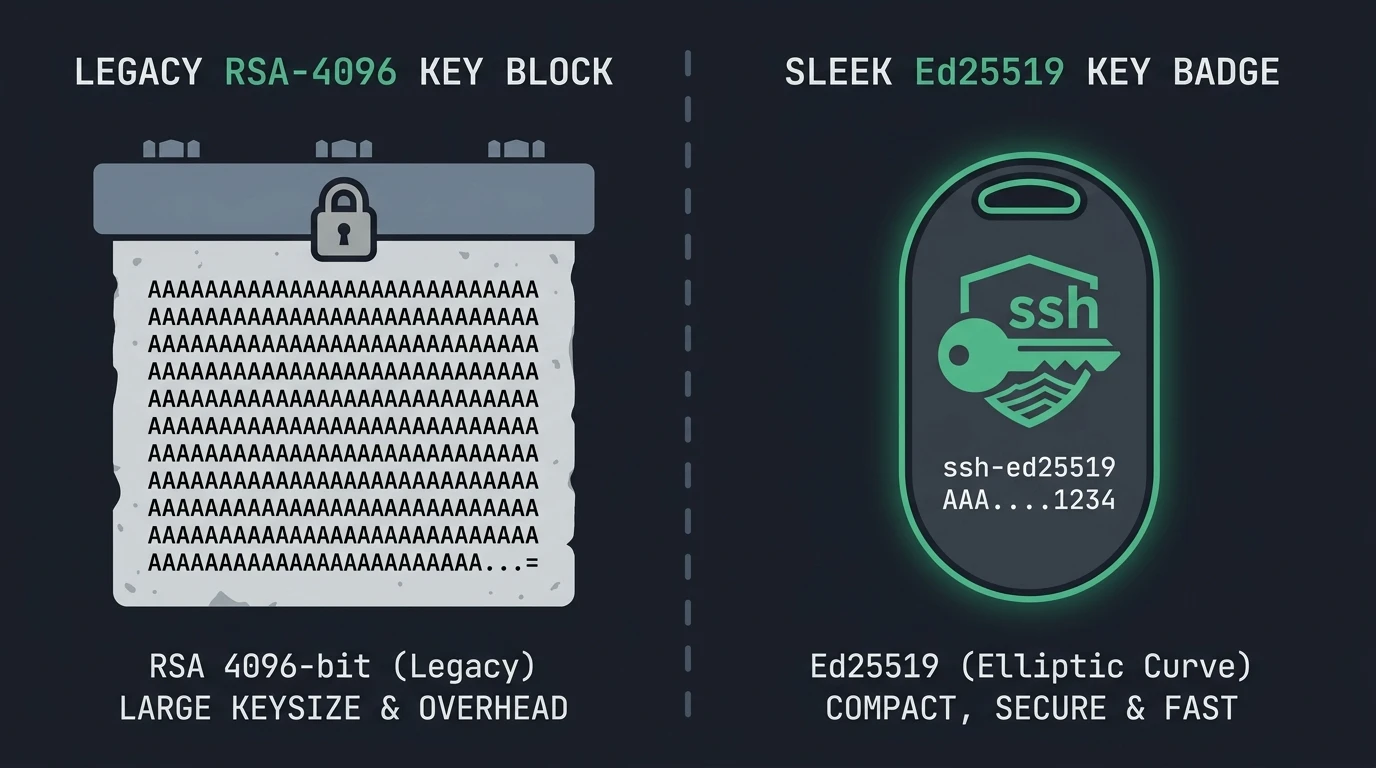
How to generate and migrate to Ed25519 SSH keys in OpenSSH, streamline your local ssh config, and handle legacy RSA SHA-1 host connections.
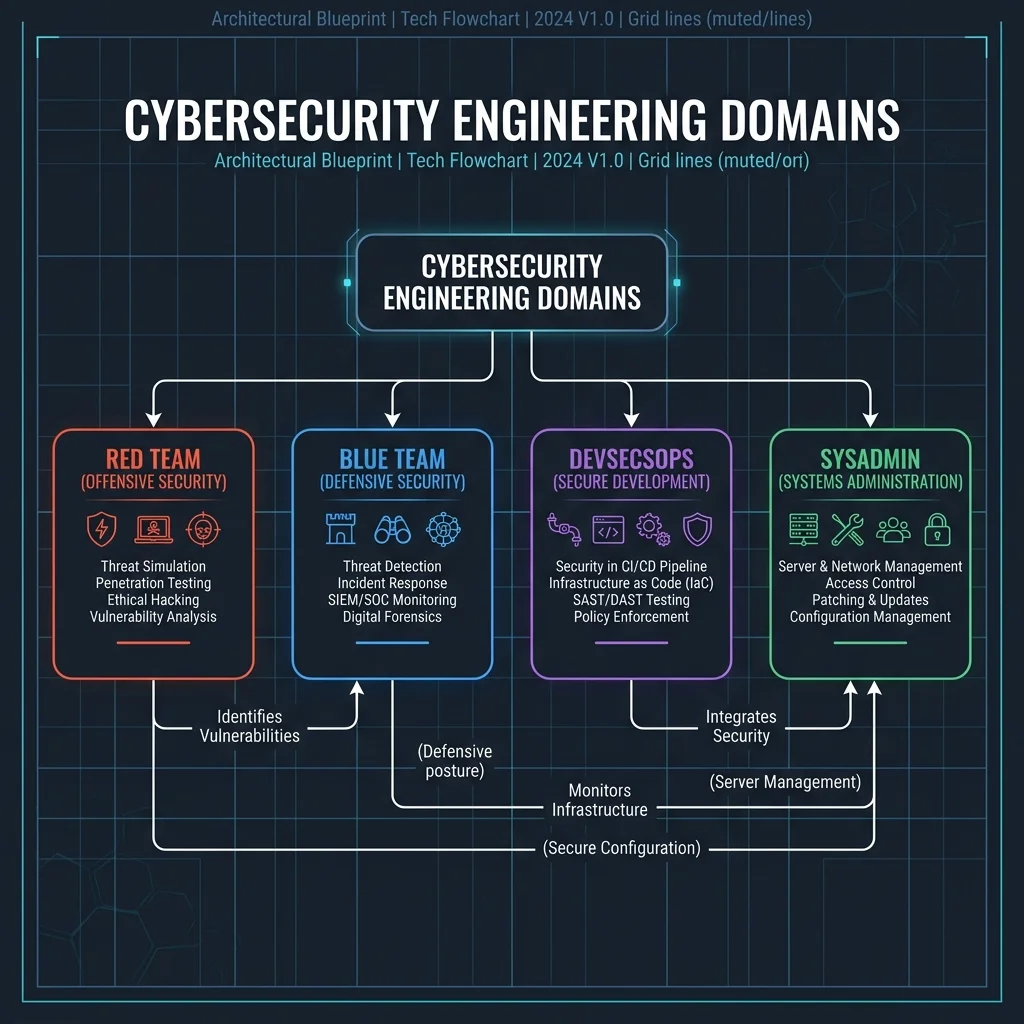
Breaking down the Cyber Security Domains mind map by Henry Jiang: career paths across security architecture, incident response, governance, and user education.
An inside look at Google's multi-layered physical and operational security measures protecting global cloud data center infrastructure.
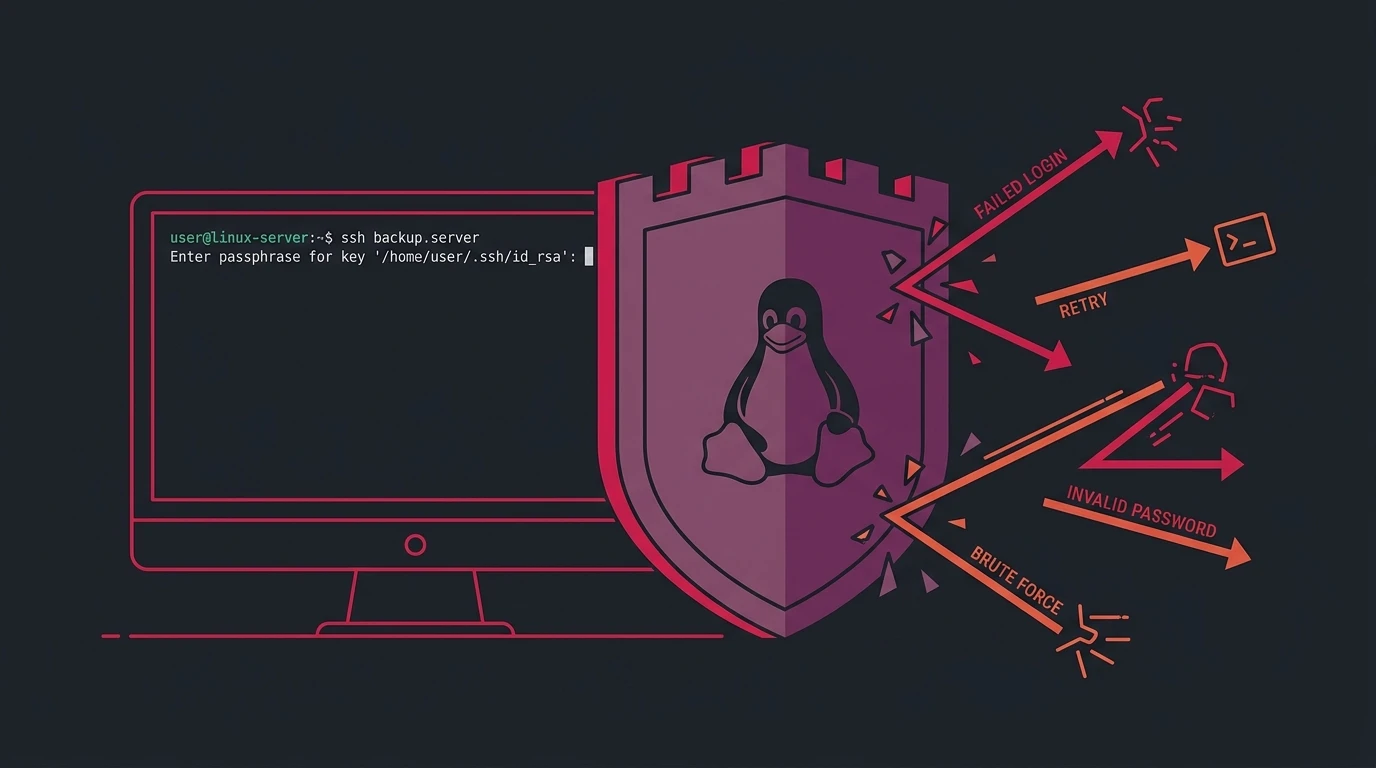
How to configure Fail2ban on Debian and Ubuntu servers with custom SSH jail rules, IP whitelisting, and quick CLI commands to manage banned IPs.
Analysis of a mobile marketing blunder where UK telecom provider Three accidentally sent adult promotional SMS messages to its customer base.
Top platforms and interactive war games for learning ethical hacking, penetration testing, and web application security skills.
The European Commission funds bug bounties on major open source projects including VLC, KeePass, 7-Zip, Apache Tomcat, and PuTTY through HackerOne.
How pam_panic provides a duress authentication module for Linux that wipes sensitive keys or triggers defensive scripts if a duress password is typed.
Building a standalone DIY security camera using a Raspberry Pi, an HC-SR501 PIR motion sensor, and automated snapshot capture with email alerts.
Looking back at mid-2000s IRC network defence: building multi-network security bots with real-time SNOTICE sniffing, Blitzed OPM lookups, and auto-G-Lines.
Essential WordPress security practices: securing wp-admin, updating plugins and themes, enforcing strong passwords, and monitoring user accounts.
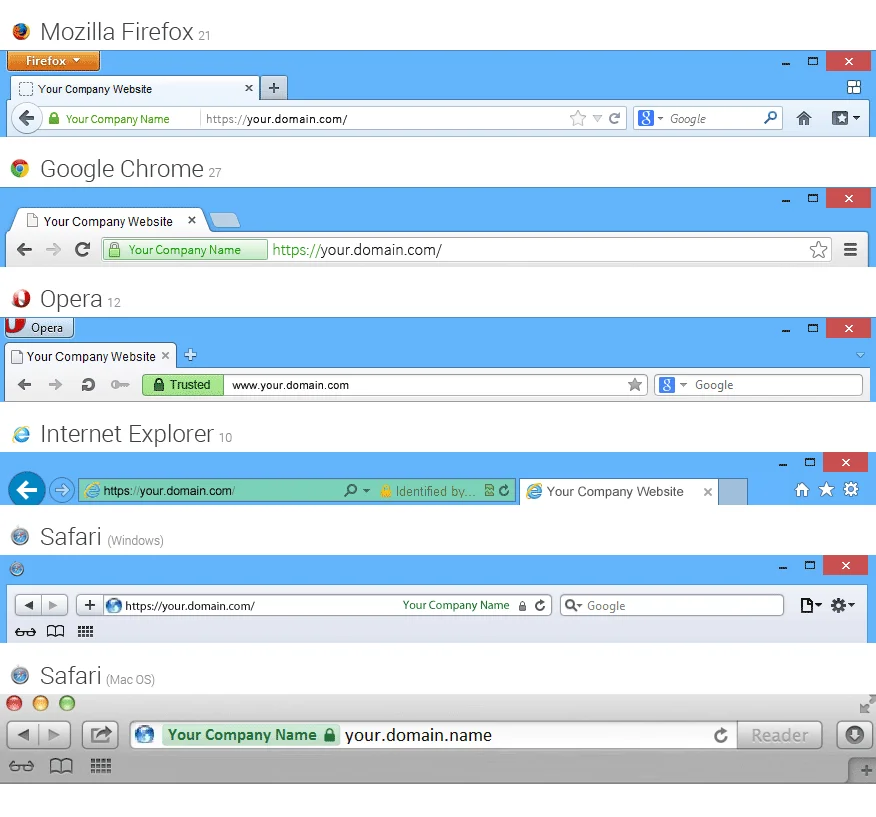
How to fix insecure HTTP mixed content warnings in WordPress posts after enabling SSL using search-and-replace queries and URL updates.
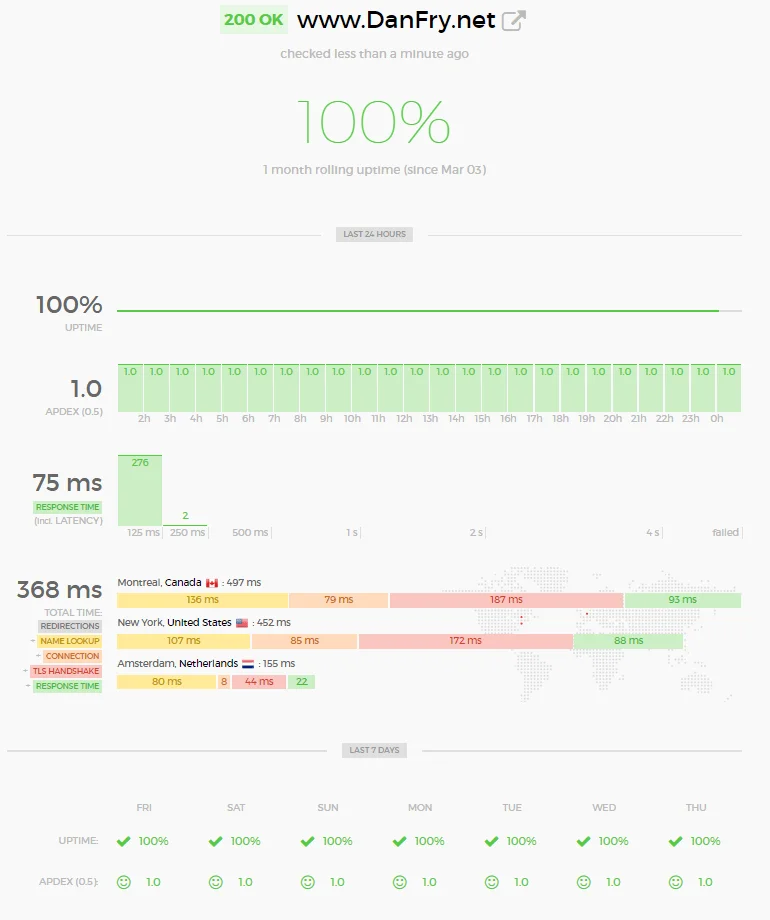
Overview of StatusCake and modern uptime monitoring services featuring public status badges, REST APIs, and multi-location ping checks.
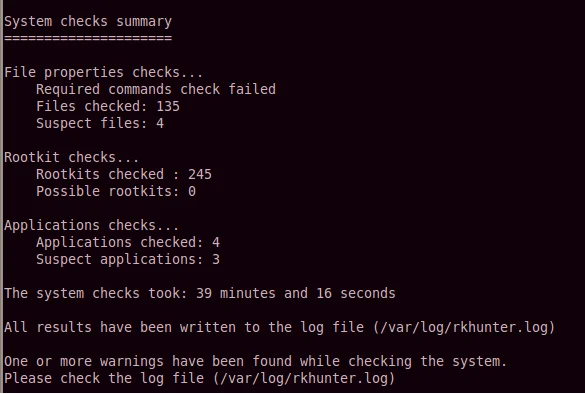
How to automate daily rootkit and malware scans on Debian/Ubuntu servers using rkhunter and chkrootkit with daily email log reports via cron.
Security audit demonstration showing how Android debug bridge (ADB) commands on Windows CLI could automate SMS messaging and testing.
How to configure instant email notifications whenever someone logs into a Linux server as root via SSH using a simple .bashrc script and mailx.